

Losses from exploits and thefts across the crypto industry hit their highest monthly total so far this year.
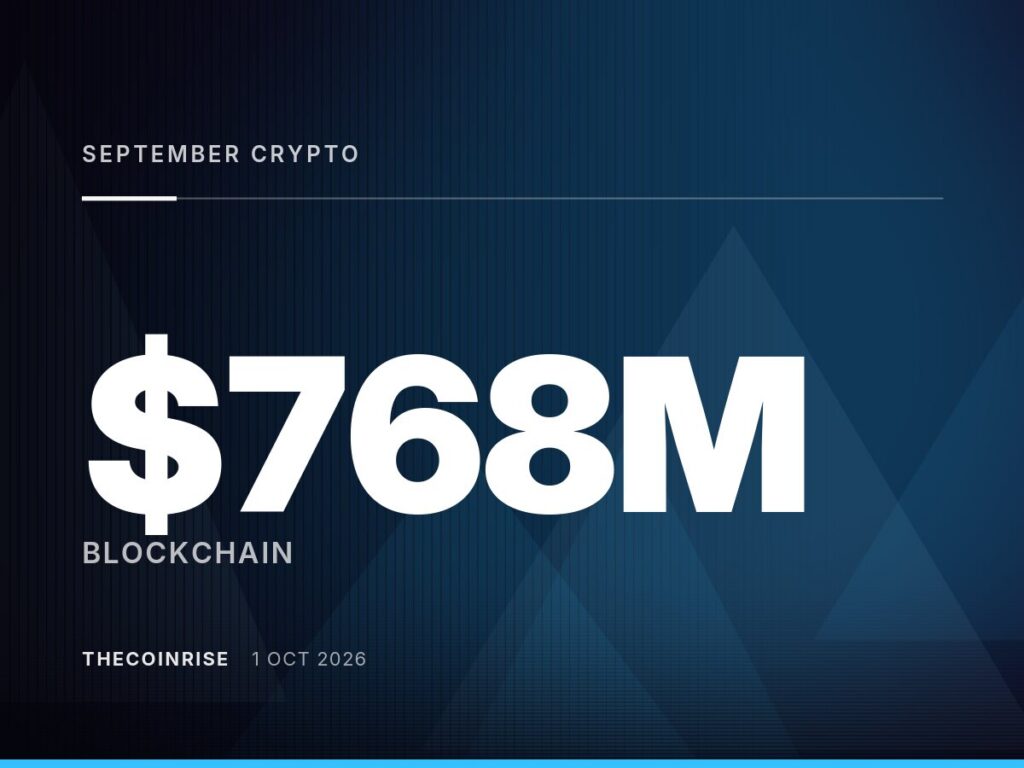
September has been confirmed as the worst month of 2026 for crypto-related theft. Reported losses from hacks and exploits across the industry topped $768 million, according to Cointelegraph. BitKE separately placed the figure above $700 million, describing the month as the most costly so far this year. Both outlets agree on the broad scale of the damage, even where the precise totals differ slightly.
Monthly tallies of crypto losses are typically compiled from publicly disclosed exploits, including attacks on decentralized finance protocols, centralized exchanges, and individual wallets. These figures can shift as investigators uncover additional details or as projects disclose losses after initial silence. Discrepancies between trackers are common, reflecting differences in methodology and timing of data collection.
The scale of September's losses places renewed attention on the security practices underpinning the digital asset industry. Despite years of warnings and repeated high-profile breaches, attackers continue to find weaknesses in smart contract code, bridge infrastructure, and custody arrangements. Each new record month reinforces concerns that security investment has not kept pace with the growth of assets held on-chain.
Crypto hacks have historically clustered around certain attack vectors. These include compromised private keys, flawed smart contract logic, and social engineering schemes targeting employees or users directly. Without granular breakdowns from the September data, it remains unclear which categories contributed most to the total losses reported this month.
The timing of this spike is notable given the broader push toward institutional adoption of digital assets. As more capital flows into crypto markets through regulated products and custody services, the stakes tied to security failures grow correspondingly larger. A single large exploit can affect thousands of users and shake confidence in platforms far beyond the one directly targeted.
Regulators and industry bodies have repeatedly called for stronger security standards, including mandatory audits, bug bounty programs, and improved incident disclosure practices. Whether September's losses prompt new policy action remains to be seen. Past spikes in hacking activity have sometimes led to voluntary industry reforms, though enforcement of security standards across a fragmented global market remains inconsistent.
For now, the September total stands as a stark reminder of the risks still embedded in crypto infrastructure. It also highlights the challenge facing both investors and platforms in distinguishing well-secured projects from those carrying hidden vulnerabilities.
Market Impact
Large-scale hacking losses tend to weigh on sentiment toward affected protocols and, at times, the broader market. Investors often reassess exposure to platforms perceived as carrying weaker security practices following high-profile incidents. Exchanges and protocols linked to September's losses may face scrutiny over their custody arrangements and incident response procedures in the weeks ahead.
The broader implication is a continued emphasis on security audits and insurance mechanisms within the industry. Institutional investors evaluating crypto allocations may factor rising hack totals into their risk assessments, particularly when considering custody providers or decentralized finance exposure. No specific market-wide price reaction has been reported in connection with the September figures.
September's losses mark a significant setback for crypto security in 2026, reinforcing calls for stronger safeguards across the industry. The full breakdown of affected platforms and attack methods may become clearer as further investigations conclude.
Frequently Asked Questions
How much was lost to crypto hacks in September?
Cointelegraph reported losses exceeding $768 million, while BitKE reported the figure surpassing $700 million, both describing it as the worst month of 2026 for crypto theft.
Why do the reported totals differ between sources?
Trackers often use different methodologies and timing when compiling hack data, which can lead to slightly different totals even when describing the same period.
What types of attacks typically drive these losses?
Past incidents have involved compromised private keys, smart contract vulnerabilities, and social engineering targeting exchange or protocol employees, though September's specific breakdown has not been detailed in current reporting.
Could September's losses affect crypto regulation?
Large hacking totals often renew calls from regulators and industry groups for stronger security standards, though any formal policy response remains uncertain at this stage.